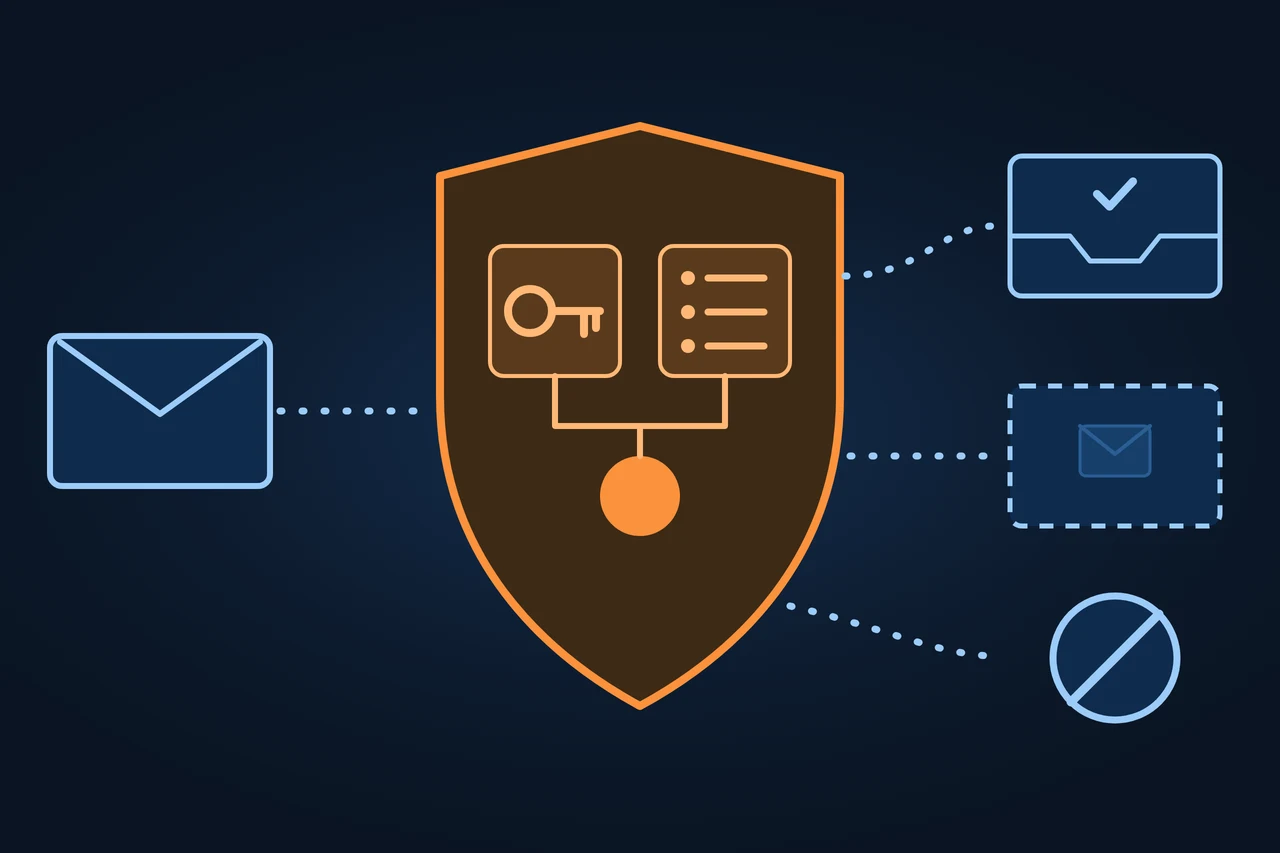
DMARC is an email standard (RFC 9989, May 2026) that lets a domain owner publish in the DNS what receiving servers should do with messages that carry the domain in the visible sender address but pass neither an aligned SPF check nor an aligned DKIM check. The same record says where to send reports.
DMARC, the RFC 9989 standard that tells receivers what to do with mail failing SPF and DKIM. Record syntax, policies, reports and Gmail's rules.
Origin of the term
DMARC stands for "Domain-based Message Authentication, Reporting, and Conformance", the title of RFC 9989. The three parts of the name match what the protocol does: it authenticates the sender's domain, sends reports back to the owner and lets the owner ask for a specific treatment of mail that does not conform.
History and development
According to dmarc.org, a group of companies began working on DMARC in spring 2011, building on efforts that started in 2010. Among them were AOL, Comcast, Gmail, Hotmail, Yahoo! Mail, Bank of America, Facebook, LinkedIn and PayPal.
30 January 2012: the first specification is published.
March 2015: it appears as RFC 7489, an Informational RFC submitted outside the IETF standards process.
July 2021: RFC 9091, an experimental RFC, adds policies for public suffix domains.
February 2024: Gmail and Yahoo start requiring DMARC from high-volume senders.
20 May 2026: the IETF publishes RFC 9989 and, for reporting, RFC 9990 and RFC 9991. DMARC moves to the Standards Track and replaces RFC 7489 and RFC 9091.
How it works
DMARC builds on two older checks. With SPF (RFC 7208), a domain lists the servers allowed to send on its behalf, and the receiver compares the sending IP address with the SPF record of the envelope domain (MAIL FROM). DKIM (RFC 6376) signs the message, and the receiver validates the signature with the public key that the domain named in the d= tag publishes in the DNS.
Neither check looks at the sender the recipient actually sees, the "From:" line. A message passes DMARC if at least one of the two checks passes for a domain that matches the "From:" domain. That match is called alignment. In relaxed mode the two domains only need to share the same organizational domain, for example news.example.com and mail.example.com. In strict mode they have to be identical. According to RFC 9989, nearly all domain owners find relaxed alignment sufficient, and it is the default for adkim and aspf.
The policy is published as a TXT record in the DNS under the name _dmarc: for example.com, at _dmarc.example.com. If the sender uses a subdomain without its own record, the receiver walks up the levels of the name with the "DNS Tree Walk" defined in RFC 9989, with at most eight queries. This method replaces the Public Suffix List that RFC 7489 relied on.
Tag
Meaning
Required
v
Version, always DMARC1
Yes
p
Policy for the domain: none, quarantine or reject
Recommended
sp
Policy for existing subdomains
No
np
Policy for non-existent subdomains
No
adkim, aspf
DKIM and SPF alignment: r (relaxed, default) or s (strict)
No
rua
Addresses for aggregate reports
No
ruf
Addresses for failure reports
No
fo
When to generate a failure report
No
t
Test mode: y applies a policy one level milder
No
psd
Marks a public suffix domain
No
Source: RFC 9989, section 4.7 and appendix C.5.
The pct, rf and ri tags are no longer part of the standard.
Both checks pass. For DMARC, only the one that matches the From domain counts
From:news.example.comthe sender the recipient sees
SPFpass
checks the envelope domain (MAIL FROM)
another domain
relaxed (default)not alignedstrictnot aligned
DKIMpass
checks the domain in the d= tag
mail.example.com
relaxed (default)alignedstrictnot aligned
relaxed (default): same organizational domain is enoughDMARC passes
strict: domains have to be identicalDMARC fails
According to RFC 9989. One aligned pass out of the two is enough.
Which domain does your DKIM signature match?
Types and variants
According to RFC 9989, with none the domain owner offers no expression of preference; with quarantine it considers failing mail suspicious; with reject it considers the failure a clear sign that the use of the domain is not valid. The RFC treats this as a preference and forbids receivers to reject a message solely because the domain publishes reject. Without further analysis they must treat it as quarantine.
With t=y a domain can test a policy without applying it fully: the receiver treats reject as quarantine and quarantine as none. Before RFC 9989, domain owners used pct=0 for this, which is why the new standard replaced pct with t.
sp applies to subdomains that exist and np to subdomains that do not exist, which an attacker can put in the sender address. If np is missing, sp applies, and if sp is missing, p applies.
Examples
A domain starting in monitoring mode publishes at _dmarc.example.com: "v=DMARC1; p=none; rua=mailto:dmarc-feedback@example.com". Receivers do not change how they handle the mail and send aggregate reports to that address. The example comes from appendix B of RFC 9989.
Next, the owner tests "v=DMARC1; p=quarantine; rua=mailto:dmarc-feedback@example.com; t=y", under which receivers still apply none. The last step in the same appendix is "v=DMARC1; p=reject; rua=mailto:dmarc-feedback@example.com", without t.
Whether a domain has DMARC shows up in a single DNS query, for example "dig TXT _dmarc.example.com" in a terminal.
How to measure it
With rua, receivers send aggregate reports in XML. According to RFC 9990 they can include the policy found, the disposition applied, the SPF and DKIM results, whether each was aligned and the message counts. RFC 9989 says receivers should send aggregate reports at least once every 24 hours. Without rua, receivers must not generate aggregate reports. Not every receiver sends them: RFC 9989 names resource limits, local policy against sharing data and user privacy as the most common reasons.
An example: a report shows 1,200 messages from the newsletter provider's IP addresses with aligned DKIM and 40 from an unknown IP address that fails everything. The 40 are either a forgotten service or spoofing. The report does not say which.
With ruf, receivers can send failure reports about individual messages (RFC 9991). These can contain header fields or the entire message and therefore personal data. According to RFC 9991, many large providers limit them or switch them off and rely on aggregate reports.
Advantages and disadvantages
Since 1 February 2024, Gmail has required DMARC from anyone sending more than 5,000 messages a day to Gmail accounts. A policy of none is enough, but the "From:" domain has to align with SPF or DKIM. According to Gmail's help, enforcement has been ramping up since November 2025, with temporary and permanent rejections. Yahoo asks bulk senders for SPF, DKIM and a DMARC record with at least p=none, but sets no number: it says explicitly that it will not specify a volume threshold. On 2 April 2025, Microsoft announced similar requirements for Outlook.com for domains sending more than 5,000 emails a day. One-click unsubscribe and spam rates are covered in the email marketing entry.
The trade-offs depend on the case:
A domain that sends a newsletter through a provider needs that provider to sign with DKIM using the domain itself; otherwise the mail is not aligned.
A domain that sends no mail can publish a strict policy without risk to its own mail, because it has none.
In an organization with many services (CRM, billing, support), the reports reveal mail streams nobody had listed. Moving to reject before fixing them blocks the organization's own mail.
For a domain whose users post to mailing lists, RFC 9989 advises against reject (section 7.4).
How it differs from related concepts
Method
What it checks
Where it lives
What it does not do alone
SPF
Whether the IP may send for the envelope domain
TXT record of the domain
Does not look at the visible "From:"
DKIM
Whether the signature of the d= domain is valid
Public key in the DNS
Does not say what to do on failure
DMARC
Whether a passing SPF or DKIM check matches "From:"
TXT record at _dmarc
Does not authenticate on its own
ARC
Which results each intermediary saw
Message header fields
Does not replace DMARC
BIMI
Displays the brand's logo
Record in the DNS
According to BIMI Group, needs DMARC at quarantine or reject
Platform for DMARC reports and managed SPF, DKIM and BIMI
Google Postmaster Tools
Spam rate, reputation and authentication of mail sent to Gmail accounts
MxToolbox
Public lookup and check of a DMARC record
Valimail
Email authentication service
Source: each tool's website, accessed 16.11.2026. Listed alphabetically.
Criticism and limits
RFC 9989 says DMARC can only directly combat spoofing of the exact domain. It does not address visually similar domain names or a false display name with a different address behind it.
Forwarding breaks SPF, because the message arrives from the forwarder's IP address; DKIM signatures generally stay valid, according to RFC 9989. ARC (RFC 8617, experimental, July 2019) is meant to help here: it records the authentication results of each intermediary, so the final receiver can see them. RFC 9989 also concedes that mail forwarded through mailing lists with an unchanged "From:" line is frequently rejected because of a reject policy. That is why section 7.4 says domains whose users post to mailing lists should not publish reject. Domains that still want it should first run p=none for at least a month, then p=quarantine for as long, and compare the reports.
How to apply it, step by step
List every service that sends mail with the domain and set up SPF and DKIM with the domain itself for each one.
Set up a mailbox or service for aggregate reports.
Publish "v=DMARC1; p=none; rua=mailto:…" at _dmarc of the domain.
Read the reports for at least a month and fix the mail streams that are not aligned.
Move to p=quarantine for an equally long period, with t=y at the start if needed.
Move to p=reject only if the reports allow it and the domain has no users who post to mailing lists.
Add np=reject for subdomains that do not exist.
Best practices
Use SPF and DKIM together, as RFC 9989 recommends; a domain that publishes reject must sign with DKIM.
Keep rua in place after reaching reject.
Publish an explicit record for every domain used in "From:".
Request failure reports only for specific diagnostics and for a short time, as RFC 9991 advises.
Common mistakes
Following a plan with pct=10, 25, 50 and 100: RFC 9989 removed pct, and t=y is the tool for testing.
Publishing two DMARC records at the same name: according to RFC 9989, the receiver discards both.
Relying on SPF alone, which usually fails when mail is forwarded.
Staying at p=none forever, a policy that asks for no treatment at all.
How this entry was made
This entry was written in November 2026 with the help of AI. The mechanism comes from RFC 9989, RFC 9990 and RFC 9991; the sending rules come from the help pages of Gmail, Yahoo and Microsoft. All sources were accessed on 16.11.2026.
Manuel Riveiro RodriguezCEO & Digital Strategist
A technical audit covers this and everything else in one pass.
Domain-based Message Authentication, Reporting, and Conformance, the standard a domain uses to say what should happen to mail that uses its name without passing aligned SPF or DKIM.
Is DMARC mandatory?
Some mailbox providers require it. Gmail does for senders of more than 5,000 messages a day to Gmail accounts, Yahoo for bulk senders without naming a number, and Microsoft for domains sending more than 5,000 emails a day to Outlook.com. In all three cases p=none is enough.
What is the difference between SPF, DKIM and DMARC?
SPF says which servers may send for a domain, DKIM signs the message, and DMARC requires one of the two to match the visible sender and says what to do if neither does.
How do I check if a domain has DMARC?
Query the TXT record at _dmarc of the domain, for example with dig TXT _dmarc.example.com, or use a public lookup tool.
What does p=none mean?
The domain owner asks for no special treatment of failing mail. It is used to collect reports before tightening the policy.
Does the pct tag still exist?
No. RFC 9989, published in May 2026, removed pct. To test a policy without applying it fully, use t=y, which lowers it by one level.